Testing Cookie Consent and Privacy Compliance Flows in 2026: How to Validate GDPR, CCPA, and DPDP Consent Gates in Automated Test Suites
Why Cookie Consent Testing Is Not Optional in 2026
Cookie consent gate testing validates that your implementation correctly blocks tracking technology on rejection, fires only after consent on acceptance, persists the consent decision across page loads and sessions, and propagates the consent signal to every integrated third-party tag. An automated consent test suite covers these behaviors using browser automation that inspects cookie stores, monitors outbound network requests for analytics tags, and asserts that consent UI states match the expected behavior for each user action — accept, reject, partial consent, and revisit.
The regulatory backdrop makes automated consent testing a business requirement rather than a quality-of-life improvement. GDPR's Article 83 permits fines up to EUR 20 million or 4% of global annual revenue for violations of consent requirements. The California Consumer Privacy Act (CCPA) and its successor CPRA set penalties of USD 7,500 per intentional violation — a figure that scales quickly when automated compliance tools discover that your opt-out signal is not honored across all third-party tags. India's Digital Personal Data Protection Act (DPDP Act, 2023) adds another compliance surface for any organization processing Indian users' personal data, requiring explicit, informed, and freely given consent before processing for purposes beyond those strictly necessary. The Data Protection Board was constituted in 2025, and enforcement actions are active.
The practical failure mode is consistent across organizations that have deployed a consent platform without testing it. A consent management tool (OneTrust, Cookiebot, Didomi, or a custom implementation) is integrated, the banner is styled and deployed, and the team marks consent integration as done. No test validates that the rejection signal actually suppresses the Google Analytics tag or Meta Pixel before they fire. No test confirms that cookies from a rejected category do not appear in the browser's cookie store after the user clicks Reject. No test verifies that consent persists across page navigation and browser sessions. The consent banner is a UI element. The consent gate is a behavior. Only tests distinguish between the two.
For teams building a complete software testing strategy, cookie consent testing belongs in the standard regression suite — not as a periodic manual audit, but as an automated check on every deployment that touches the consent configuration, tag manager setup, or analytics integration. A change to a Google Tag Manager container, a new analytics vendor added to the platform, or an A/B testing tool integration can silently bypass an existing consent gate without triggering any existing test.
What Cookie Consent Testing Actually Covers Across GDPR, CCPA, and DPDP
The three major privacy frameworks that affect most web applications in 2026 have different consent models. Understanding what each framework requires you to test is prerequisite to designing a consent test suite that covers actual compliance risk rather than visual smoke tests.
| Framework | Consent Model | What Must Be Tested | Common Failure Mode |
|---|---|---|---|
| GDPR (EU) | Opt-in. Explicit prior consent required for non-essential cookies. No pre-ticked boxes. Equal prominence for accept and reject. | Banner loads before analytics tags fire. Reject blocks all non-essential cookies. Accept stores valid consent cookie. Consent is granular by category. Withdrawal is as easy as grant. | Analytics tag fires on page load before banner interaction. Reject button harder to find or absent. |
| CCPA / CPRA (California) | Opt-out. Data processing is allowed by default; users opt out via Do Not Sell or Share link. GPC signal must be honored automatically. | Do Not Sell link present and functional. GPC header signal triggers opt-out automatically without manual interaction. Opt-out persists across sessions. Targeted advertising tags disabled after opt-out. | GPC signal not read server-side. Opt-out stored in browser only — lost on cookie clear. Advertising tags continue firing after opt-out. |
| DPDP (India) | Opt-in. Explicit, informed, and freely given consent required. Notice must specify purpose. Right to withdraw consent must be provided. | Consent notice includes processing purpose. Consent is positive and specific — no implied or bundled consent. Withdrawal mechanism is accessible and functional. Processing stops within defined timeframe after withdrawal. | Purpose description absent or vague. Single consent covers multiple unrelated purposes. Withdrawal path not surfaced in account settings. |
These frameworks are not interchangeable from a testing perspective. A test suite designed for GDPR compliance — which focuses on blocking tags before consent is given — does not fully cover CCPA compliance, which requires validating that GPC signals are honored automatically without user interaction. A complete consent test suite for an application serving users across these jurisdictions covers all three sets of requirements, with jurisdiction-specific test variants where the consent flow differs by geography.
For teams whose applications serve Indian users specifically, DPDP adds a requirement that is often missed: the consent notice must specify the processing purpose clearly enough that a reasonable user understands what they are consenting to. This is not a behavior that UI automation can verify automatically — it requires a manual review step combined with automated verification that the consent action triggers the expected data processing behavior. The test automation services at Astaqc include DPDP-specific test design as part of privacy compliance testing engagements.
Building a Cookie Consent Test Suite: The Core Scenarios
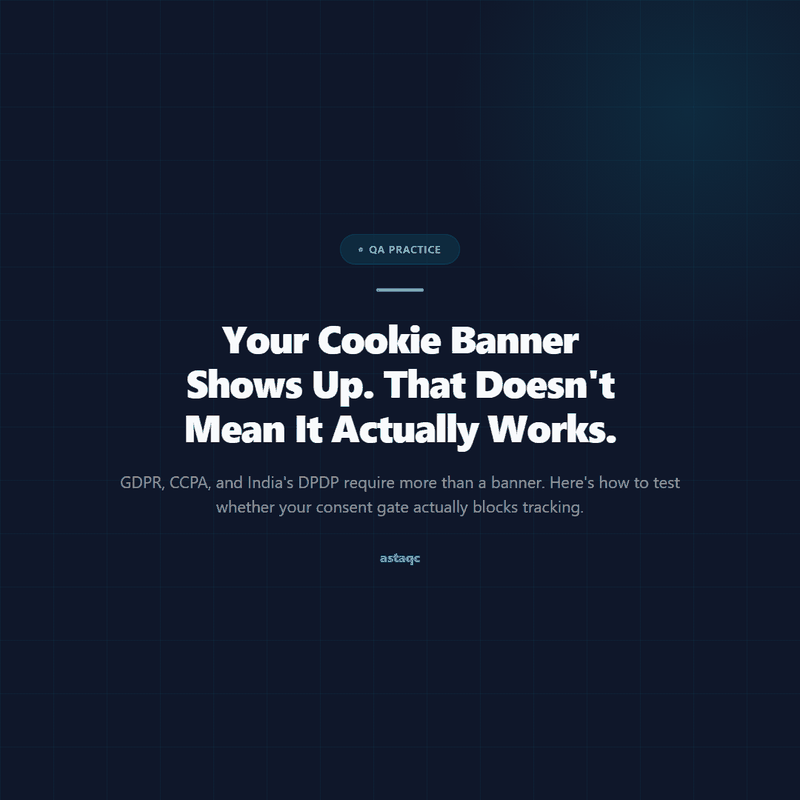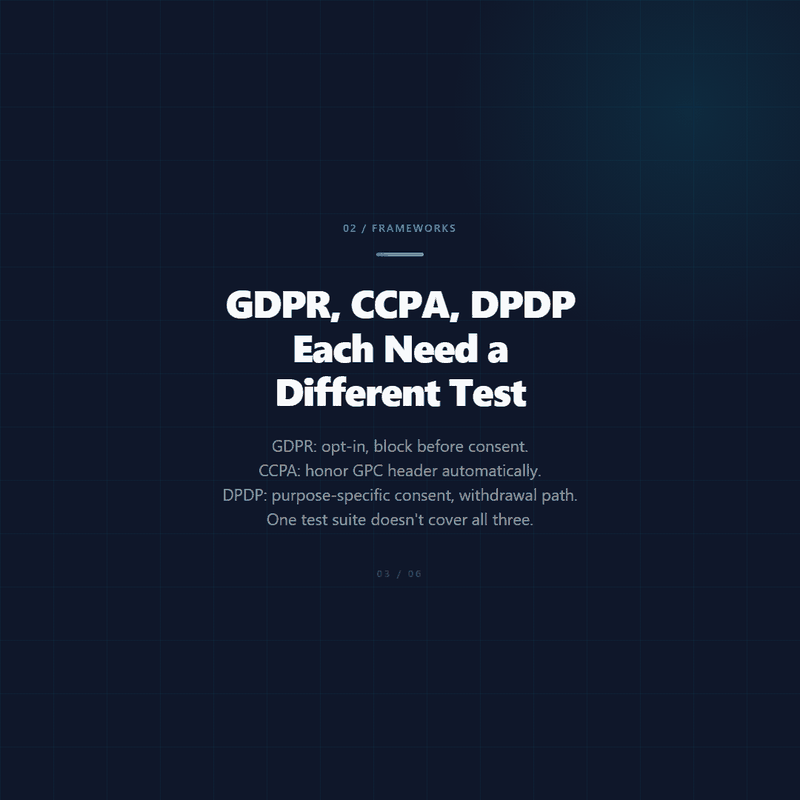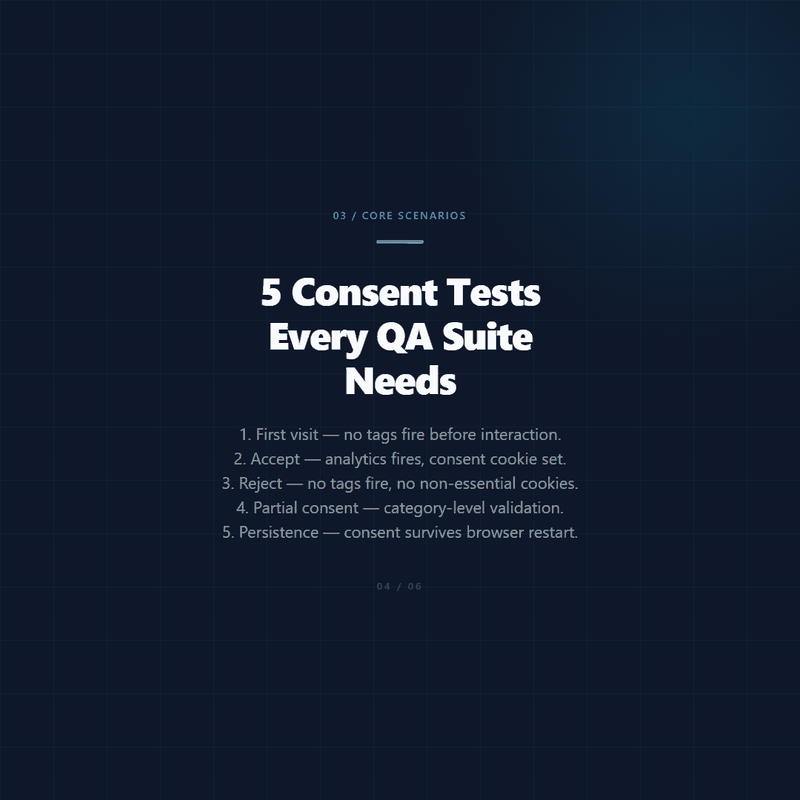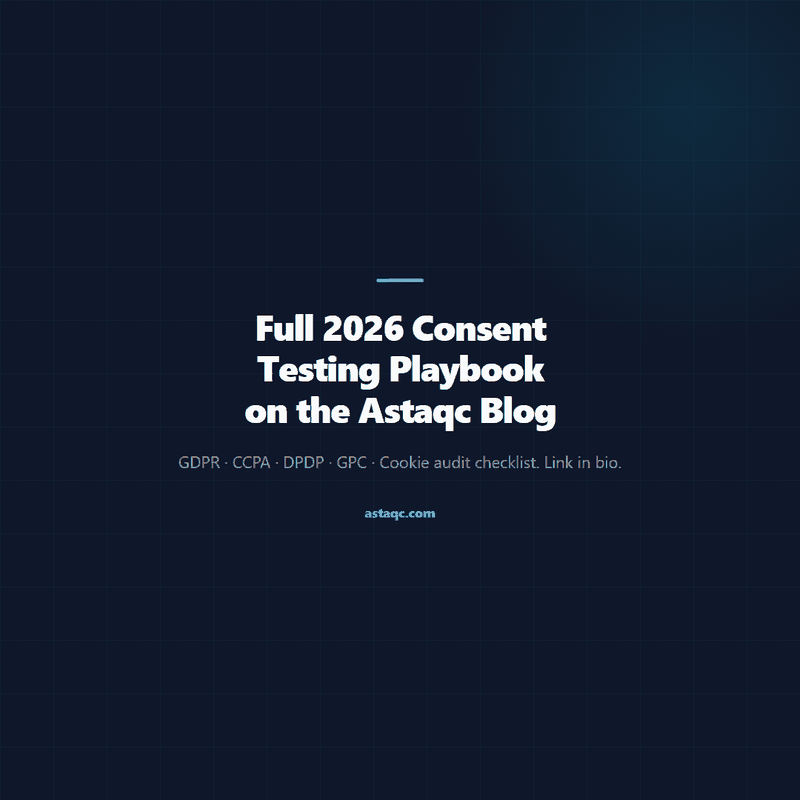
A consent test suite that covers actual compliance risk — rather than just confirming that a banner appears — requires five core scenario sets. Each scenario maps to a distinct consent behavior that regulations require and that implementation bugs routinely break.
Scenario 1: First Visit — Banner Display and Tag Blocking
On first visit, before any user interaction with the consent banner, no non-essential tracking tags should fire. The test sequence: navigate to the page in a clean browser profile with no existing consent cookies, intercept outgoing network requests, assert that no requests to analytics or advertising domains are made before the consent banner interaction. Tools for this assertion range from browser network monitoring in Playwright and Selenium to dedicated consent audit tools. The passing condition is zero analytics tag requests before the user clicks Accept.
This scenario catches the most common and highest-risk failure mode: analytics tags configured to fire immediately on page load, with the consent check happening asynchronously in the tag manager after the initial page request has already been sent.
Scenario 2: Accept All — Tag Firing and Cookie Verification
After clicking Accept All, all consented analytics and advertising tags should fire, and the consent cookie should be set with the correct category flags. The test: click Accept, then assert that the analytics tag fires (verify the network request to the analytics domain), that the consent cookie is present in the browser's cookie store, and that the cookie's value encodes consent for the expected categories. For GDPR implementations, check that the consent expiry is within the platform's stated duration (typically 1–2 years) rather than a session cookie that resets on browser close.
Scenario 3: Reject All — Tag Suppression and Cookie Absence
After clicking Reject All, no analytics or advertising tags should fire, and no non-essential cookies should be present in the browser's cookie store. The test: click Reject (or Decline), then assert that the analytics domain network request is absent, that the ad platform pixels are absent, and that the browser's cookie store contains only strictly necessary cookies (session identifiers, CSRF tokens, authentication). This is the scenario most likely to fail silently — many consent implementations set the consent cookie on Reject but do not actually suppress tag firing, because the tag manager's trigger conditions are not properly gated on the consent signal.
Scenario 4: Partial Consent — Category-Specific Tag Behavior
When a user accepts analytics cookies but rejects advertising cookies, analytics tags should fire and advertising pixels should not. The test: open the consent preference center, enable Analytics and disable Advertising, save preferences, then assert that the analytics network request is present and the advertising pixel request is absent. This scenario validates category-level granularity, which GDPR requires explicitly — a consent implementation that bundles all non-essential cookies into a single Accept/Reject choice does not satisfy the granularity requirement for most DPAs' interpretations.
Scenario 5: Consent Persistence and Withdrawal
Consent should persist across page navigation and browser sessions. After accepting cookies, navigate to a different page and verify that the analytics tag fires immediately without displaying the consent banner again. After closing and reopening the browser with the consent cookie intact, verify the same. Additionally, test the withdrawal path: navigate to the consent management link in the site footer, withdraw consent for analytics, and verify that analytics tag firing stops and the consent cookie is updated. For manual testing workflows, withdrawal testing is a good candidate for structured exploratory testing alongside automated coverage, since the withdrawal UI often has usability issues that automated assertions miss but that users encounter immediately.

Implementation Failure Modes That Automated Consent Testing Catches
The consent testing scenarios above are designed to catch the specific implementation failures that organizations encounter in practice. Each failure mode corresponds to a distinct technical mechanism that causes compliance violations despite a correctly configured consent banner UI.
Tags Fire Before Consent Is Given
The most common failure: analytics or advertising tags configured as page-level triggers in Google Tag Manager fire before the consent signal is available. This happens because GTM loads and evaluates triggers synchronously, while the consent platform's JavaScript evaluates asynchronously after the GTM container loads. The result is a narrow window — typically 100–500ms on a fast connection — where analytics tags fire before the consent gate is active. Automated testing with network request monitoring catches this by asserting that no analytics requests are made in a clean browser profile before the user interacts with the consent banner, including requests made in the first 2–3 seconds of page load.
Reject Signal Not Propagated to Tag Manager
The user clicks Reject, but the consent platform's opt-out signal is not wired to the tag manager's consent mode or trigger conditions. The consent cookie is set with the correct Reject value, but the tag manager evaluates its own internal consent state rather than reading the platform's cookie — and because the tag manager's consent state was never updated, analytics tags continue to fire. This failure is invisible to any test that only checks whether the consent cookie is set. It requires the test to monitor outbound network requests and assert that analytics tag requests are absent after Reject, not just that the consent cookie contains the expected value.
Consent Not Persisted Across Sessions
The user accepts cookies, closes the browser, reopens it the next day, and sees the consent banner again. This happens when the consent decision is stored in sessionStorage rather than a persistent cookie, or when the consent cookie's domain or path attributes are set incorrectly — for example, a cookie set on www.example.com that is not present on example.com or on a subdomain like app.example.com. Automated testing catches this by: (a) accepting consent, (b) closing the browser profile and reopening it, (c) asserting that the consent banner does not appear on the next visit and that analytics tags fire immediately without user interaction.
First-Party Cookie Bypass
Some analytics implementations set first-party cookies that are classified as "strictly necessary" in the consent configuration but actually contain advertising identifiers or cross-site tracking data. These cookies are set even after Reject because the consent gate only blocks the tag that sets them if the tag is classified as non-essential — if the classification is wrong, the tag fires. Catching this requires comparing the cookies set after Reject against an approved list of strictly necessary cookies, asserting that no unexpected identifiers are present. For teams running AI-assisted testing approaches, cookie classification audits are a good use case for automated analysis against a known-good baseline, since the volume of cookies across a large site makes manual review impractical.
Automated consent testing is a specialized area where the technical complexity of network request monitoring, cookie store inspection, and cross-session state validation exceeds standard UI testing. Teams building consent test suites from scratch benefit from working with experienced QA teams — Astaqc's QA team services include consent gate testing design as part of compliance testing engagements for GDPR, CCPA, and DPDP scopes.
Frequently Asked Questions
What browser automation approach works best for cookie consent testing?
Playwright and Selenium are both suitable for consent gate testing because they support network request interception, cookie store inspection, and clean browser profiles. Playwright's built-in context.route() and request event listeners make network monitoring straightforward without additional tooling. Selenium requires a separate proxy layer (mitmproxy, BrowserMob) for request interception, which adds complexity but works reliably. For teams using TestInspector, the HTTP request step and cookie assertion steps in a no-code test sequence cover the core consent scenarios — banner interaction, cookie verification, and basic tag suppression checking — without writing test code. For advanced network-level assertion (verifying pixel payloads rather than just request presence), code-first tools provide more granular control.
How often should consent tests run?
Consent tests should run on every deployment that modifies the consent configuration, tag manager container, analytics integration, or any JavaScript file loaded before the consent gate initializes. For organizations using a consent management platform (CMP), also run consent tests after any CMP version upgrade, since platform updates can alter how the consent signal is propagated to tag manager. A lightweight smoke test — banner appears, Reject blocks analytics, Accept fires analytics, consent cookie is set — should run in under 60 seconds and belongs in every CI/CD pipeline as a post-deployment gate. Full regression coverage including category-level assertions and cross-session persistence can run nightly.
How do you test GPC (Global Privacy Control) signal handling for CCPA?
GPC testing requires sending the Sec-GPC: 1 HTTP header with the initial page request and verifying that the site responds by setting an opt-out state without user interaction. In Playwright, set custom headers in the browser context before navigating: context.setExtraHTTPHeaders({'Sec-GPC': '1'}). After page load, assert that advertising and targeting cookies are absent, that the opt-out cookie is set with the correct value, and that advertising pixel requests are blocked. The GPC test must verify server-side handling, not just client-side: some implementations read GPC in the browser and update client-side tag manager state, which can be bypassed by direct API calls that don't send the header. See the testing strategy guide for context on how to combine automated GPC testing with manual verification of server-side log analysis.
What consent testing tools exist beyond browser automation?
Beyond Playwright and Selenium-based testing, several specialized tools support consent audit workflows. CookieChecker and Cookiebot's self-audit tools scan for cookies set before consent on first visit, flagging non-essential cookies that appear in a clean profile before any user interaction. The Consent Management Platform vendors (OneTrust, Cookiebot) provide their own audit dashboards that log consent events and flag anomalies. OWASP's web testing guide includes a privacy testing checklist that covers consent banner implementation alongside broader privacy controls. For DPDP-specific requirements, India's Data Protection Board has published compliance guidance that specifies what constitutes valid consent notice and how withdrawal must be implemented — these requirements inform the test design for the purpose-specificity and withdrawal scenarios described above.
What is the relationship between consent testing and accessibility testing?
Cookie consent banners are frequently inaccessible. Common issues include focus not being trapped in the banner modal (allowing keyboard users to interact with the page behind the banner before consenting), Reject buttons with insufficient color contrast relative to Accept buttons (which GDPR enforcement bodies have flagged as making rejection disproportionately difficult), and consent forms that are not navigable by screen reader. Accessibility testing for consent banners is distinct from functional consent testing but should run alongside it: a banner that is visually present but keyboard-inaccessible fails both GDPR's equal prominence requirement and WCAG 2.1 success criteria for modal dialogs. TestInspector's axe-core accessibility assertions cover the WCAG violations in the consent banner UI, complementing the functional consent gate tests in the same test suite. For structured test automation services that include accessibility and consent testing in a combined audit, Astaqc offers combined QA engagements covering both dimensions.
5 consent test scenarios every QA suite needs in 2026.
A cookie consent banner that appears is not the same as a consent gate that works. Only an automated test suite distinguishes between the two — and only the second one satisfies a regulator.
Astaqc Team
November 17, 2026


Published by the Astaqc engineering team. Astaqc Consulting is a software testing company based in India, delivering test automation, manual testing, and performance testing services.